How to Know Which Cipher Is Used Console Linux
To know details about the encryption ciphers that are used by the HMC run the following lshmcencr commands. Using FTP Logon you are able to check.

Osint Spy Search Using Osint Open Source Intelligence Best Hacking Tools Open Source Intelligence Learn Facts
This cipher is also used for conventional encryption if --personal-cipher-preferences and --cipher-algo is not given.

. A SFTP connection can be selected based on the connection type. The latter includes TLS key exchange authentication encryption and mac algorithms used along with any key size restrictions and whether the algorithm is classed as an export cipherNote that without the -v option ciphers may seem to appear twice in a cipher list. Each active connection may use a difference cipher based on the combination of.
Gpg -d gpg. List the encryption ciphers that are used by HMC to encrypt user password. Refer the documentation to capture the traffic.
-ssl3 SSL3 mode. New TLSv13 Cipher is TLS_AES_128_GCM_SHA256. So listing Apache supported ciphers is done using nmap as follow.
This will describe the version of TLS or SSL used. 6 Double click the line containing the Client Hello. In order to decrypt the file you just encrypted using your key you have to use the gpg command with the -d option for decrypt.
The default cipher is CAST5. So below we know the connection from 100231 is done using deepak user while for other two hosts root user was used for connecting to node3. Use name as the cipher algorithm used to protect secret keys.
Expand Secure Sockets Layer Cipher Suites. Echo Cipher Text gpg -d OutFile. Lshmcencr -c passwd -t c.
Click on Mount Points and. How Do I Know Which Cipher Is Sftp Using. A the capabilities on the server b the capabilities of the client c cipher preference of the server and client.
This is when similar. I cannot find any information on how to update or add either specific or all ciphers to. -tls1 TLS1 mode.
Open the command line and run the following command. Use name as the digest algorithm used to mangle the passphrases. Cat InFile gpg -d OutFile.
Twofish has a block size of 128bits. To decrypt use the command. Click Analyze - Decode As - Transportselect the port and the select SSL apply and the save the settings.
The server should accept and use the provided cipher in the connection. Now to verify TLSv13 support on your server or website run the following command. Test your hostname using SSLLABS or Scan your server using NMAP See also Connect to Exchange Server on-premises Dynamics 365 Server-side sync Exchange server TLS guidance Cipher Suites in TLSSSL Schannel SSP.
Openssl ciphers -v. Then you should see messages as. The format for the sslciphersuite option in this file is.
If you are interested in HTTPS. If you are using Apache and e-Commerce you probably want to know all the details of the ciphers used by the Apache SSL module. Now click on More Information.
Decrypt andor verify the contents of File. On CentOSRed Hat based distributions. To verify that your server complies with the security protocol you can perform a test using a TLS cipher and scanner tool.
Use the domain name of the server or website that you are. In the address bar click the icon to the left of the URL. Cat InFile gpg -d.
Decrypt andor verify Cipher Text and write the result to OutFile. It can encrypt whole disks removable media partitions software RAID volumes logical volumes and. Look for the response of the client hello message in the captured traffic.
While I have correctly configured the apache openssl settings to pass a scan these settings have effectively limited the client browsers that can securely transact on the sites https side. List ciphers with a complete description of protocol version SSLv2 or SSLv3. Gpg -d filetxtgpg CAMELLIA256 Cipher.
If modifying or specifying the cipher list for a TLSv12 connection the -cipher flag is used instead of the -ciphersuites flag. Click on Full Disk Encryption then System Settings. These are the ciphers cipher suites that the client supports.
Key Exchange Algorithms RSA DH ECDH DHE ECDHE PSK AuthenticationDigital Signature Algorithm RSA ECDSA DSA Bulk Encryption Algorithms AES CHACHA20 Camellia ARIA. At the right-top device encryption status and progress will show if the drive is encrypted. Where specifies the ciphers that are allowed disallowed and.
Click on a drive in the Mount Points folder to obtain information about how a drive is encrypted and the status of the encryption process. The omiserverconf file is located in the directory etcoptomiconf. From the drop down listings you can see the encryption MAC key-exchange and public key algorithms.
The below commands can be used to list the ciphers. Your question and your goal arent necessarily related. This is where SSLTLS handshake is done.
Decrypt andor verify Cipher Text. 5 Find the Client Hello and the Server Hello methods. -v verbose mode a textual listing of the SSLTLS ciphers in OpenSSL.
-V even more verbose. Openssl ciphers -help. None preauth Saying what CipherReviews.
Briefly enter the ciphers you want to use. Gpg --symmetric --cipher-algo TWOFISH filetxt. This call gives you a complete list of all the ciphers currently accepted by your running version of Apache.
Rootnode3 last -a grep -i still deepak pts1 Fri May 31 1658 still. In this case you will be prompted with a window that contains many more information more specifically the key used. Look for the Technical details section.
Using this command you can also get the information about the user using which the SSH connection was created between server and client. If we want to provide a list of ciphers they can be delimitered with a colon. Once the traffic is captured.
Dm-cryptLUKS dm-crypt is a transparent disk encryption subsystem in Linux kernel v26 and later and DragonFly BSD. VeraCrypt It is free open-source disk encryption software for Windows 7VistaXP Mac OS X and Linux based on TrueCrypt codebase. 7 Examine the Client Hello information that pops up in a separate window.
The default algorithm is SHA-1. Decrypt andor verify the contents of File and write the result to OutFile. You need to set the LogLevel DEBUG in the server sshd_config.
Looking at any individual connection will not tell you if your SSL configuration is optimal. On UbuntuDebian based distributions. The captured traffic will be shown as SSL.
RHEL CentOS and other flavors of Linux usrbinopenssl ciphers -v Cipher Suites are named combinations of. In gpg if TWOFISH is used as the algorithm it uses a key size of 256bits 32 bytes To encrypt using the Twofish cipher which is considered strong use the following command. Select the Security tab.
If your corporate standards requires the use of a different set of ciphers run the chhmcencr command to modify the encryption ciphers. We are using Centos 65 Final OpenSSL 101e-fips 11 Feb 2013. Sudo apt install openssl.
Sudo yum install openssl.

How Can I Enable Elliptical Curve Cryptography Ecc Ciphers In Websphere Application Server 8 5

Enable Tlsv1 2 And Approved Ciphers For Ibm Control Center
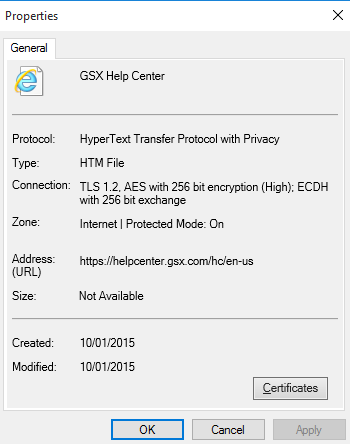
How To Identify The Cipher Used By An Https Connection Gsx Help Center

How To Identify The Cipher Used By An Https Connection Gsx Help Center
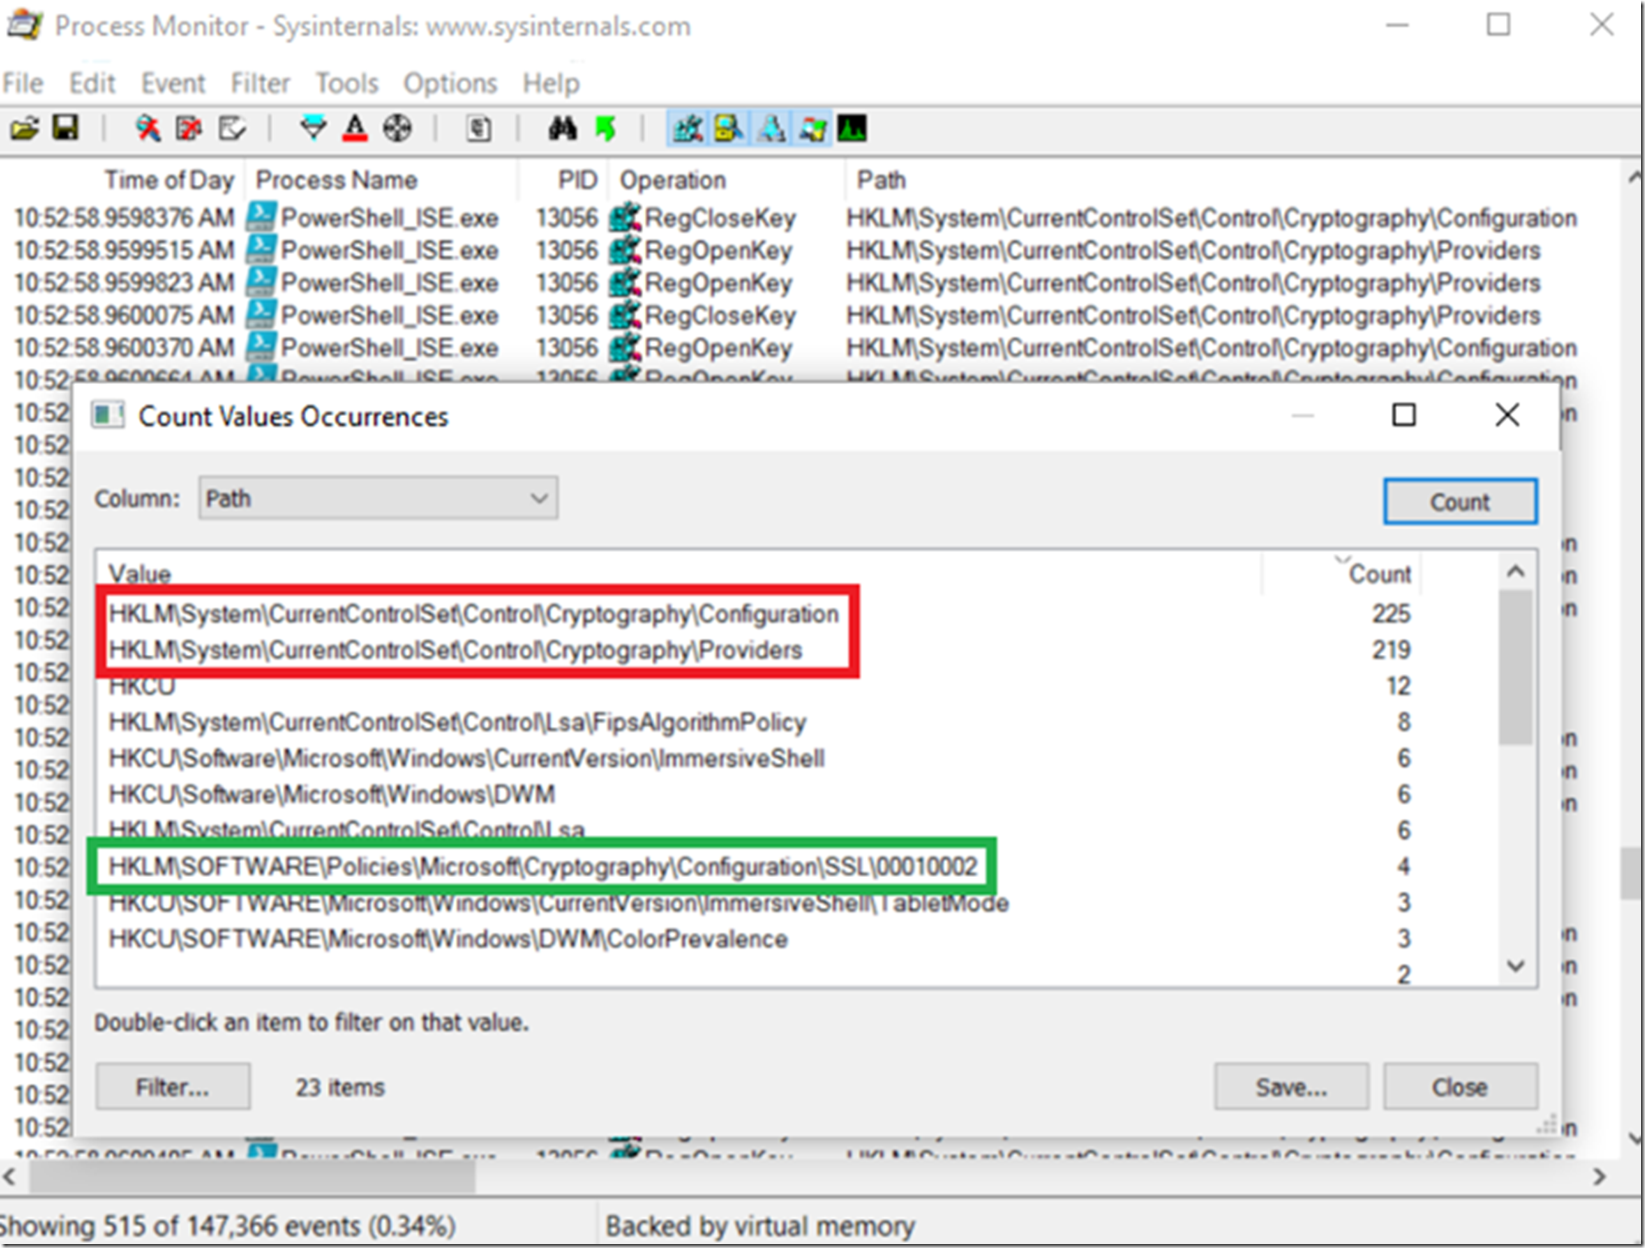
How To See The Cipher Suites On An Azure App Service The Best C Programmer In The World Benjamin Perkins
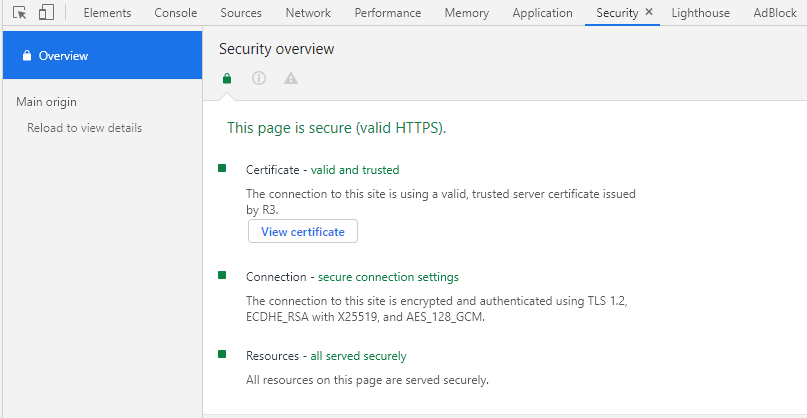
How To Identify The Cipher Used By An Https Connection Gsx Help Center
How To Check Ssl Ciphers In Linux Certsimple Com

The Openssl Command Line Tool

How To Test A Server For Tls 1 2 1 3 Support In Linux Devanswers Co


Comments
Post a Comment